
AI agents are moving from generating text to taking real actions inside companies, from editing code and accessing files to calling APIs and interacting with business systems. That growing autonomy is creating a new security challenge, because an agent can have valid credentials and still make an action that was never intended. German AI security company Kontext is tackling that gap with technology designed to decide whether an agent should be allowed to act before the action takes place.
$4 Million Funding
Kontext has raised $4 million in funding in a round led by 42CAP, with participation from Andreessen Horowitz’s a16z CSX and High Tech Gründerfonds, or HTGF.
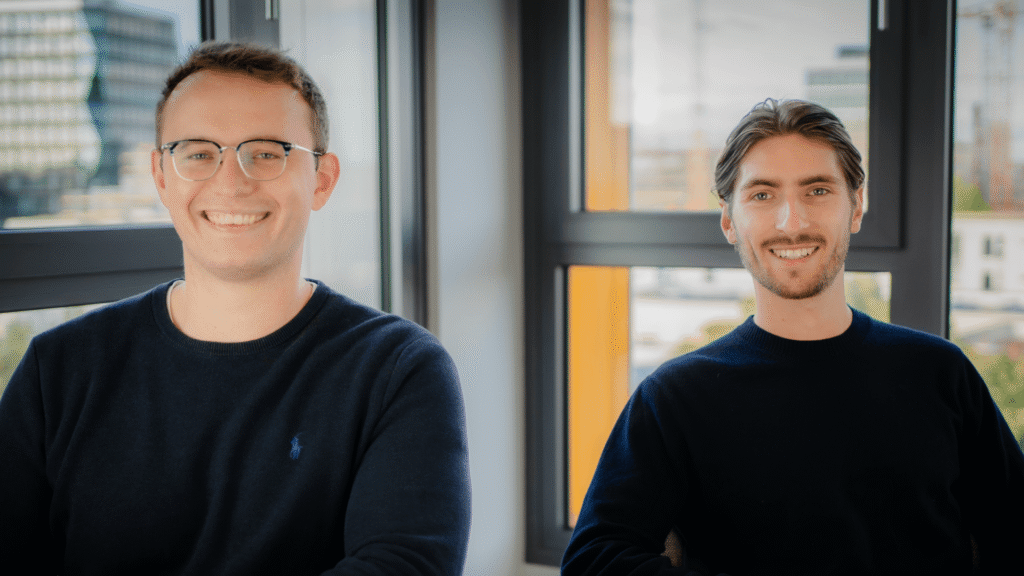
The company was founded by Jens Ernstberger and Michel Osswald, who bring experience across secure computing, applied cryptography and AI systems. The new capital will support the expansion of Kontext’s engineering team, continued development of its runtime security platform and customer deployments.
Kontext is building what it describes as runtime authorization infrastructure for AI agents. Its platform is designed to enforce security policies at the point where an agent is about to perform an action, rather than relying solely on permissions assigned earlier.
A New AI Security Problem
Traditional access controls can answer whether a user or application generally has permission to access a particular system. AI agents introduce a more complicated question: whether a specific action should be allowed at a particular moment.
An agent might be authorised to access GitHub, for example, but that does not necessarily mean it should delete a repository, modify a protected branch or expose sensitive information.
Kontext evaluates factors including the user, agent session, tool, resource, requested action, parameters, policy and risk context before an action executes. The company says its approach is designed to provide security teams with a control point for autonomous software activity.
Security at the Action Boundary
The company’s technology sits directly between an AI agent and the tools it wants to use. Kontext says its platform can check tool calls from AI coding environments and other agent systems before they are executed.
Its current platform supports AI agents running through environments including Claude Code, Codex and Cowork. The system can operate locally, evaluate tool calls in milliseconds and record decisions for later review.
This approach is particularly relevant as businesses give AI agents access to production systems, internal files, software repositories and other resources.
Observe Before You Enforce
Kontext has designed its platform to allow organisations to start in an observation mode rather than immediately blocking activity.
In observe mode, the platform records what it would allow, question or deny based on configured policies. Security teams can then review real agent behaviour and adjust their controls before moving into enforcement.
Once enforcement is activated, the system can block certain actions, request human approval for higher risk operations and retain an audit trail showing what happened and why.
Controlling AI Credentials
Another part of Kontext’s platform focuses on credentials. AI agents often need access tokens or API keys to interact with external services, but long lived credentials can create a large security risk if they are exposed or misused.
Kontext is developing a credential broker that provides short lived, scoped credentials at runtime. The company says this approach keeps broad standing credentials out of agent environments and connects access to specific tasks and policies.
Building the AI Security Layer
The company’s broader thesis is that AI agent security requires more than authentication. An organisation needs to know which agent is acting, who it is acting for, what it is attempting to do and whether that action matches the approved task.
Kontext says its platform records this information in auditable traces, giving security teams visibility into agent activity and the reasoning behind individual access decisions.
With its latest $4 million funding, Kontext plans to expand its engineering capabilities and continue developing runtime controls for increasingly autonomous AI systems.
As AI agents gain the ability to operate across software, cloud infrastructure and business applications, Kontext is betting that security will need to move closer to the moment an action happens, creating a new control layer between autonomous AI and the systems it can access.